EasyDMARC
Migrate from EasyDMARC without a reporting gap
 ChatGPT
 Claude
 Gemini
 Perplexity
 Grok
In brief
To migrate from EasyDMARC, add a second rua address, compare both tools for 30 days, then replace the _dmarc CNAME it hosts. Steps for TXT and CNAME.

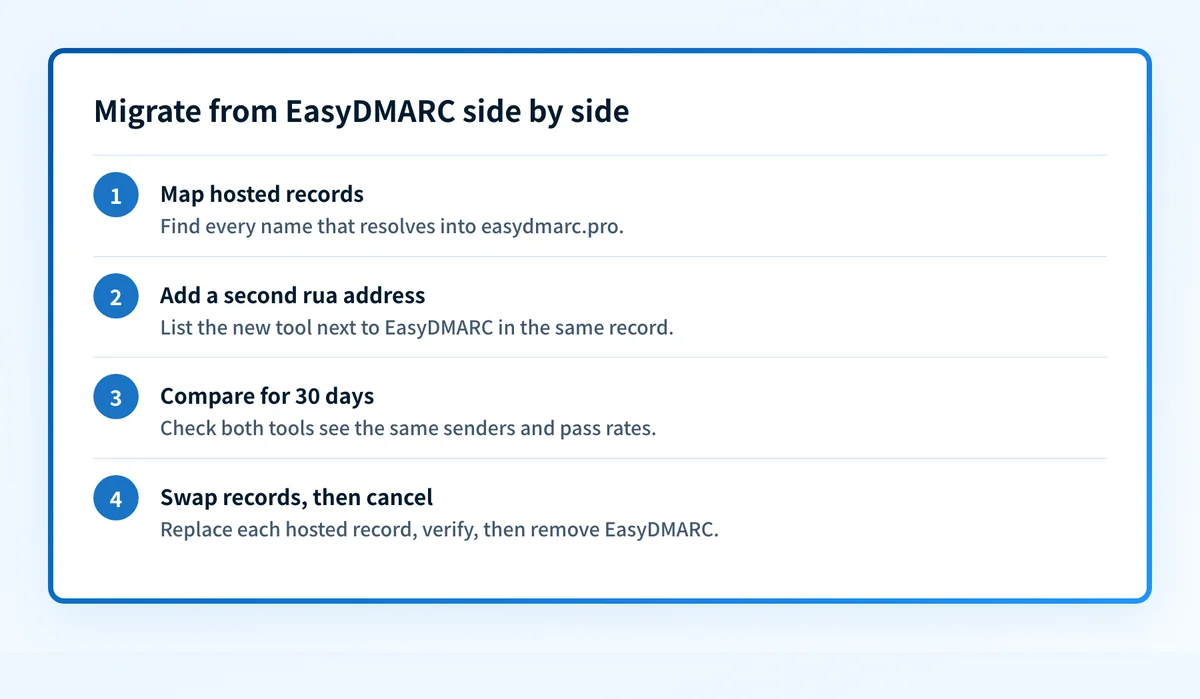
To migrate from EasyDMARC without losing reports, run the new tool beside it first. Add the new provider's reporting address to the same DMARC record so both tools receive aggregate reports, compare them for about 30 days, and only then replace any record EasyDMARC hosts for you, such as a _dmarc CNAME that points into _d.easydmarc.pro.
The order matters because EasyDMARC can host more than your DMARC record. If you cancel first, a hosted SPF include, DKIM delegation, MTA-STS policy, TLS reporting address or BIMI record can stop resolving with it.
At a glance
Quick takeaways
- A DMARC record can list more than one aggregate-report address, so two tools can read the same reports at once.
- If
_dmarcis a CNAME into EasyDMARC, add the second address inside EasyDMARC's Managed DMARC settings, or replace the CNAME with a TXT record you control. - Never publish a TXT record beside a CNAME at the same name.
- Check every name EasyDMARC may host before you cancel:
_dmarc, the SPF include,_domainkey,_mta-sts,mta-sts,_smtp._tlsanddefault._bimi. - Keep the policy tags (
p,sp,np,adkim,aspf, plus anypct,foorrialready present) exactly as they are during the move. A provider change is not a policy change.
Step 1: Find out what EasyDMARC hosts for the domain
EasyDMARC's managed records point from your zone into zones it runs, mostly by CNAME. EasyDMARC's own domain shows the pattern. On 13 November 2026, _dmarc.easydmarc.com was a CNAME to _dmarc.easydmarc_com._d.easydmarc.pro, its SPF record carried include:_spf.easydmarc_com._d.easydmarc.pro, its _mta-sts, mta-sts, _smtp._tls and default._bimi names were CNAMEs into easydmarc.pro, and _domainkey.easydmarc.com was delegated by NS record to ns.dkim.easydmarc.pro. The dots in the domain become underscores in the targets. EasyDMARC's Managed DKIM page describes the DKIM setup as a one-time _domainkey NS delegation.
Run the same lookups for your own domain. Replace example.com with it.
dig +short CNAME _dmarc.example.com
dig +short TXT _dmarc.example.com
dig +short TXT example.com | grep spf1
dig +short NS _domainkey.example.com
dig +short CNAME _mta-sts.example.com
dig +short CNAME mta-sts.example.com
dig +short CNAME _smtp._tls.example.com
dig +short CNAME default._bimi.example.com
Any answer that contains easydmarc.pro is a record EasyDMARC hosts. Write each one down with the record it replaces. If _domainkey returns an NS answer in easydmarc.pro, every DKIM selector for the domain is served from EasyDMARC's zone, not yours.
If _dmarc returns a TXT record with no CNAME, you manage the record yourself and Step 2 is a one-line edit.
Step 2: Add the second reporting address
The rua tag takes a comma-separated list of addresses (RFC 9989, section 4.7), so both tools can receive the same aggregate reports. In Palisade, the domain's Manage DMARC page shows the generated record to copy (Palisade docs).
When you manage the TXT record yourself, keep every tag and add the second address after the first:
_dmarc.example.com TXT "v=DMARC1; p=quarantine; rua=mailto:abc123@rua.easydmarc.com,mailto:your-palisade-address@reports.example"The addresses above are placeholders. Copy the real ones from each tool.
When _dmarc is a CNAME into EasyDMARC, the TXT record lives in EasyDMARC's zone, so you cannot edit it at your DNS provider. You have two options:
- Add Palisade's address inside EasyDMARC. Its Managed DMARC page says you "Configure RUA, RUF, fo, ri from the same UI" as the rest of the record. EasyDMARC's help center describes the policy controls on the Managed DMARC page under Managed Solutions (EasyDMARC help).
- Replace the CNAME with a TXT record you control. Copy the current policy exactly from
dig +short TXT _dmarc.example.com, add the second address, delete the CNAME, and publish the TXT record in one change.
Reports sent to an address on another domain need that domain's permission (RFC 9990, section 4). EasyDMARC's Managed DMARC page makes the same point about external rua destinations. If no reports reach Palisade after two days, confirm the address was copied exactly, then contact Palisade support.
Step 3: Compare both tools for about 30 days
Aggregate reports usually arrive once a day from each mailbox provider, so a month gives you enough days to see every regular sender, including monthly billing and newsletter runs. During the overlap:
- Confirm both tools list the same sending sources and roughly the same message counts.
- Compare pass and fail rates for each sender. A large gap points to a parsing or identification difference worth understanding before you switch.
- Save any EasyDMARC history you need to keep, if your plan offers an export. Do not assume another tool can import it.
- Leave the policy alone. If a policy change is due, make it before or after the move, not during it.
Step 4: Swap the hosted records, then cancel
Move one hosted record at a time, starting with _dmarc, and keep EasyDMARC active until each replacement resolves.
- DMARC. Replace the
_dmarcCNAME with the new provider's hosted record or your own TXT record. Keep the same policy tags, including anypct: receivers that still honourpctwill apply the policy to all mail if you drop it. In Palisade, hosted DMARC is a CNAME delegation, and a diff preview shows what changes before you apply it (Palisade hosted DMARC docs). - SPF. Replace the EasySPF include with the full list of senders it covered, or with the new provider's hosted SPF include. Check the result stays under the 10-lookup limit.
- MTA-STS. Repoint the
mta-stshost first. Wait untilhttps://mta-sts.example.com/.well-known/mta-sts.txtserves the new policy with a valid certificate, and check itsmxlines match your current MX records. Some hosts, Palisade included, only issue that certificate after the CNAME points to them. Then repoint_mta-sts, which changes theid. RFC 8461 asks for the HTTPS policy to be updated before the TXT record (RFC 8461, section 8.1). - BIMI. Set up the logo record at the new provider, then repoint the
default._bimiCNAME in one change. - TLS reporting. Delete the
_smtp._tlsCNAME and publish the new provider'sv=TLSRPTv1; rua=...TXT record in the same change. With Palisade, TLS reporting is a TXT record in your own zone, not a CNAME. - DKIM. If
_domainkeyis delegated to EasyDMARC, removing that NS record removes every selector under it at once. If the new home is another provider's delegated zone, publish each live selector there first, then switch the NS delegation in one change; Palisade's hosted DKIM is also a_domainkeyNS delegation, so a move to Palisade works this way. If the new home is your own zone, remove the NS record and add each selector in the same change, recreated exactly as it is now (a TXT key, or a CNAME where the sender publishes its key that way). Keep EasyDMARC active until the old NS record's TTL has passed. No DNS query lists every selector, so build the list first from the DKIM selectors in the aggregate reports collected during the overlap, EasyDMARC's Managed DKIM selector list and each sender's setup docs. A missed selector fails DKIM for that sender (Palisade hosted DKIM docs). - Verify, then cancel. Run the lookups from Step 1 again. When nothing returns
easydmarc.pro, remove EasyDMARC's addresses fromruaandrufand cancel on your schedule.
What changes for an MSP moving many client domains
The method is the same for every client domain, so an MSP can batch it. Group domains by what EasyDMARC hosts: domains with a TXT record you control need only the rua edit, while domains with a _dmarc CNAME need either the change inside EasyDMARC or a record swap. Run the 30-day overlap for a whole group at once, and move the hosted records group by group.
For the general provider-change checklist, including rollback records and change approvals, see the DMARC provider migration guide, and for DMARC basics the DMARC learning hub. For how EasyDMARC and Palisade compare on price and MSP terms, see the EasyDMARC alternative comparison. For what EasyDMARC charges and what changed in V3, see EasyDMARC pricing explained and the EasyDMARC review.
Related EasyDMARC guides
- EasyDMARC alternative for MSPs: Palisade compared
- EasyDMARC pricing: what the MSP and business plans publish
- EasyDMARC review: what V3 changed and who it fits
- DMARC reporting service: EasyDMARC vs PowerDMARC vs Palisade
- EasyDMARC vs dmarcian compared
- Valimail vs EasyDMARC compared
Evidence
Sources and further reading
- EasyDMARC Managed DMARC
- EasyDMARC help: changing the policy when the record is an EasyDMARC CNAME
- EasyDMARC help: setting up Managed DMARC from scratch
- RFC 9989: DMARC
- RFC 9990: DMARC aggregate reporting
- EasyDMARC Managed DKIM
- RFC 2181: Clarifications to the DNS specification
- RFC 8461: SMTP MTA Strict Transport Security
- Palisade docs: hosted DKIM
- Palisade docs: updating your DMARC record on your DNS provider
- Palisade docs: hosted DMARC
Questions readers ask
Frequently asked questions
Can I run Palisade and EasyDMARC at the same time?
Yes. A DMARC record's rua tag can list both tools' reporting addresses, so Palisade and EasyDMARC each receive the same aggregate reports. If EasyDMARC hosts the record through a CNAME, add Palisade's address in EasyDMARC's Managed DMARC settings or replace the CNAME with a TXT record that lists both.
How do I know if EasyDMARC hosts my DMARC record?
Run dig +short CNAME _dmarc.yourdomain.com. If the answer contains _d.easydmarc.pro, EasyDMARC hosts the record and the policy is edited in its dashboard, not at your DNS provider. A TXT answer with no CNAME means you manage the record yourself.
How long should EasyDMARC and the new tool run side by side?
Run EasyDMARC and the new tool side by side for about 30 days. Aggregate reports usually arrive daily, and a month covers monthly senders such as billing and newsletter platforms, so both tools have seen the same full set of sources before you move any hosted record.
Will I lose my DMARC report history when I leave EasyDMARC?
Your EasyDMARC plan's data-history window limits what you can save: 3 months on DMARC Plus, 1 year on Premium and the MSP plan. EasyDMARC does not say what happens to history after you cancel, so save what you need first, if your plan offers an export, and ask the new provider whether it can import it.
Does moving off EasyDMARC change my DMARC policy?
No. Moving off EasyDMARC does not change your DMARC policy as long as you keep p, sp, np, adkim and aspf, plus any pct, fo or ri tags, exactly as they are when you add the second address or replace the CNAME. Changing provider and changing policy are separate changes, and doing both at once makes any delivery problem harder to trace.
Written by
Samuel ChenardCEO & Co-Founder, Palisade
Samuel Chenard is the CEO and co-founder of Palisade, agentic DMARC software for IT teams and MSPs, from one domain to thousands.
More from Samuel →