
DMARC deployment without hand-editing DNS.
Palisade publishes your SPF, DKIM, DMARC, BIMI and MTA-STS records into your own DNS, across 64 providers. You approve the exact record; nothing waits on a ticket.
- Setting up acme-corp.com: its email-authentication records are unconfigured, and instead of setting them up by hand you choose Configure.
- Palisade recognises Cloudflare as the provider answering for the domain, and you sign in once in Cloudflare’s own window. No password is shared with Palisade, and it keeps no access afterwards.
- The exact records are shown as a before-and-after diff: the SPF value gaining a sender, plus new DKIM and DMARC records. Nothing is published until you press Approve and publish.
- Every record is live and verified in your own zone, monitoring stays on, and only the records you approved were written.
What Smart DNS Deployment helps you accomplish
The last mile is where DMARC dies
Knowing is not the same as publishing. Palisade's State of DMARC 2026 scan of the top 100,000 domains found 24.1% of domains with DMARC (13,928) collect the reports, can see exactly what is wrong, and still block nothing. The report is not the bottleneck. The DNS edit is.
You approve, Palisade publishes
Every change arrives as a record diff: the value now, the value proposed, and one button. Nothing reaches your zone until you accept it, and Palisade writes only email records into it.
Works across a mixed estate
Free DMARC reporting from a DNS host only helps for the domains already parked there. Palisade recognises whichever provider answers for each domain and publishes there, so a portfolio spread across five registrars is one workflow.
Trusted by leading brands worldwide
Works with the DNS manager you already have
Palisade recognises the provider answering for each domain and publishes there. These are the twelve most common; the full list is below.
GoDaddy
Cloudflare
Namecheap
Amazon Route 53
Squarespace
Wix
IONOS
Hostinger
Bluehost
HostGator
OVH
Network Solutions
See all 64 providers with automatic setup
123-Reg
Alibaba Cloud
All-Inkl
Aruba
Arsys
ClouDNS
Crazy Domains
Domain.com
DigitalOcean
DNSimple
DreamHost
Dynadot
EasyDNS
Enom
Fasthosts
Freename
Gandi
GreenGeeks
Hetzner
Home.pl
Hosting.com
Hostpoint
Hover
Inmotion Hosting
IWantMyName
LocaWeb
Mijndomein
Name.com
Namebright
NameSilo
Netlify
O2switch
One.com
Openprovider
OpenSRS
Papaki
Porkbun
Register.com
Register.it
Registro.br
Shopify
Simply
SiteGround
Spaceship
Strato
TransIP
United Domains
Vercel
Web.com
Wordpress.com
World4You
Xneelo
Counted 2026-08-19. Providers are added upstream, so the list grows without a change here. If yours is not on it, the record is still written out in full for you to paste, and Palisade confirms when it goes live.
From report to published record
Sign in at your provider when you publish, or connect a Cloudflare, GoDaddy or Amazon Route 53 account once. Either way, every fix becomes a review-and-approve.
Palisade recognises your provider
Palisade checks which DNS provider answers for the domain and recognises it. When you publish, you sign in once in that provider's own window, and Palisade never sees the password and keeps no access afterwards. On Cloudflare, GoDaddy or Amazon Route 53, you can connect the account ahead of time instead, with a token or AWS role you create.
The Agent drafts the fix
A new sender needs DKIM, an SPF source changed, a policy step is ready. The work arrives as a ticket with the exact record already written, not as a task telling you to go write one.
You approve the exact record
The ticket shows the current value and the proposed value side by side. Nothing is published until you accept it, and every approval is recorded.
Palisade publishes and verifies
The approved record is written into your own zone through the sign-in or account connection you authorised. Monitoring then confirms receivers can resolve it, so a change that silently failed becomes a ticket instead of a surprise.
What access this actually grants
The question every security team asks first, answered before you connect anything.
| What Palisade can write | Palisade writes only email records: SPF, DKIM, DMARC, BIMI, MTA-STS and TLS-RPT, the CNAME or NS records that delegate them, and your mail provider's MX when you ask it to set up mail. |
|---|---|
| Who authenticates | You do. With the one-time sign-in you approve the records in your provider's own window, and Palisade never sees the password and keeps no access afterwards. An account connection for Cloudflare, GoDaddy or Amazon Route 53 uses a token or AWS role you create. For Cloudflare and GoDaddy, Palisade stores the token encrypted with AWS KMS and only ever shows its last four characters. For Route 53, it stores no AWS keys at all. |
| What triggers a write | Your approval, every time. The Agent drafts the record and shows the before-and-after; no record reaches your zone unapproved. |
| Reversibility | The one-time sign-in leaves no access to revoke. Disconnect an account connection in Palisade, or revoke its token or role at the provider, whenever you like. Records already published stay in your zone. They are yours, written into your own DNS. |
| Your registrar and nameservers | Unchanged. Nothing is transferred and Palisade never takes over your zone; the records simply stop being typed by hand. |
| If your provider isn't supported | The record is still written out in full, ready to paste, and monitoring confirms when it goes live. |
What you get
One-click publishing into your own DNS
Each approved record is written into your zone at your own provider. No values typed by hand.
Automatic provider detection
Palisade works out which provider answers for each domain before you start, so you know which path is open to you.
Record diffs before every write
Current value, proposed value, one approval. The diff is the unit of work, so nothing changes without being read first.
Email-only writes, revocable access
Palisade writes only email records into your zone. The one-time sign-in keeps no access afterwards, and an account connection ends when you disconnect it or revoke its token or role.
Portfolio publishing for MSPs
200 client domains at five auth records each is 1,000 hand-edits across a dozen provider dashboards, redone every time a sender changes. This is the alternative.
Post-publish verification
Monitoring confirms receivers can resolve each record after it lands, so a change that did not take becomes a ticket.
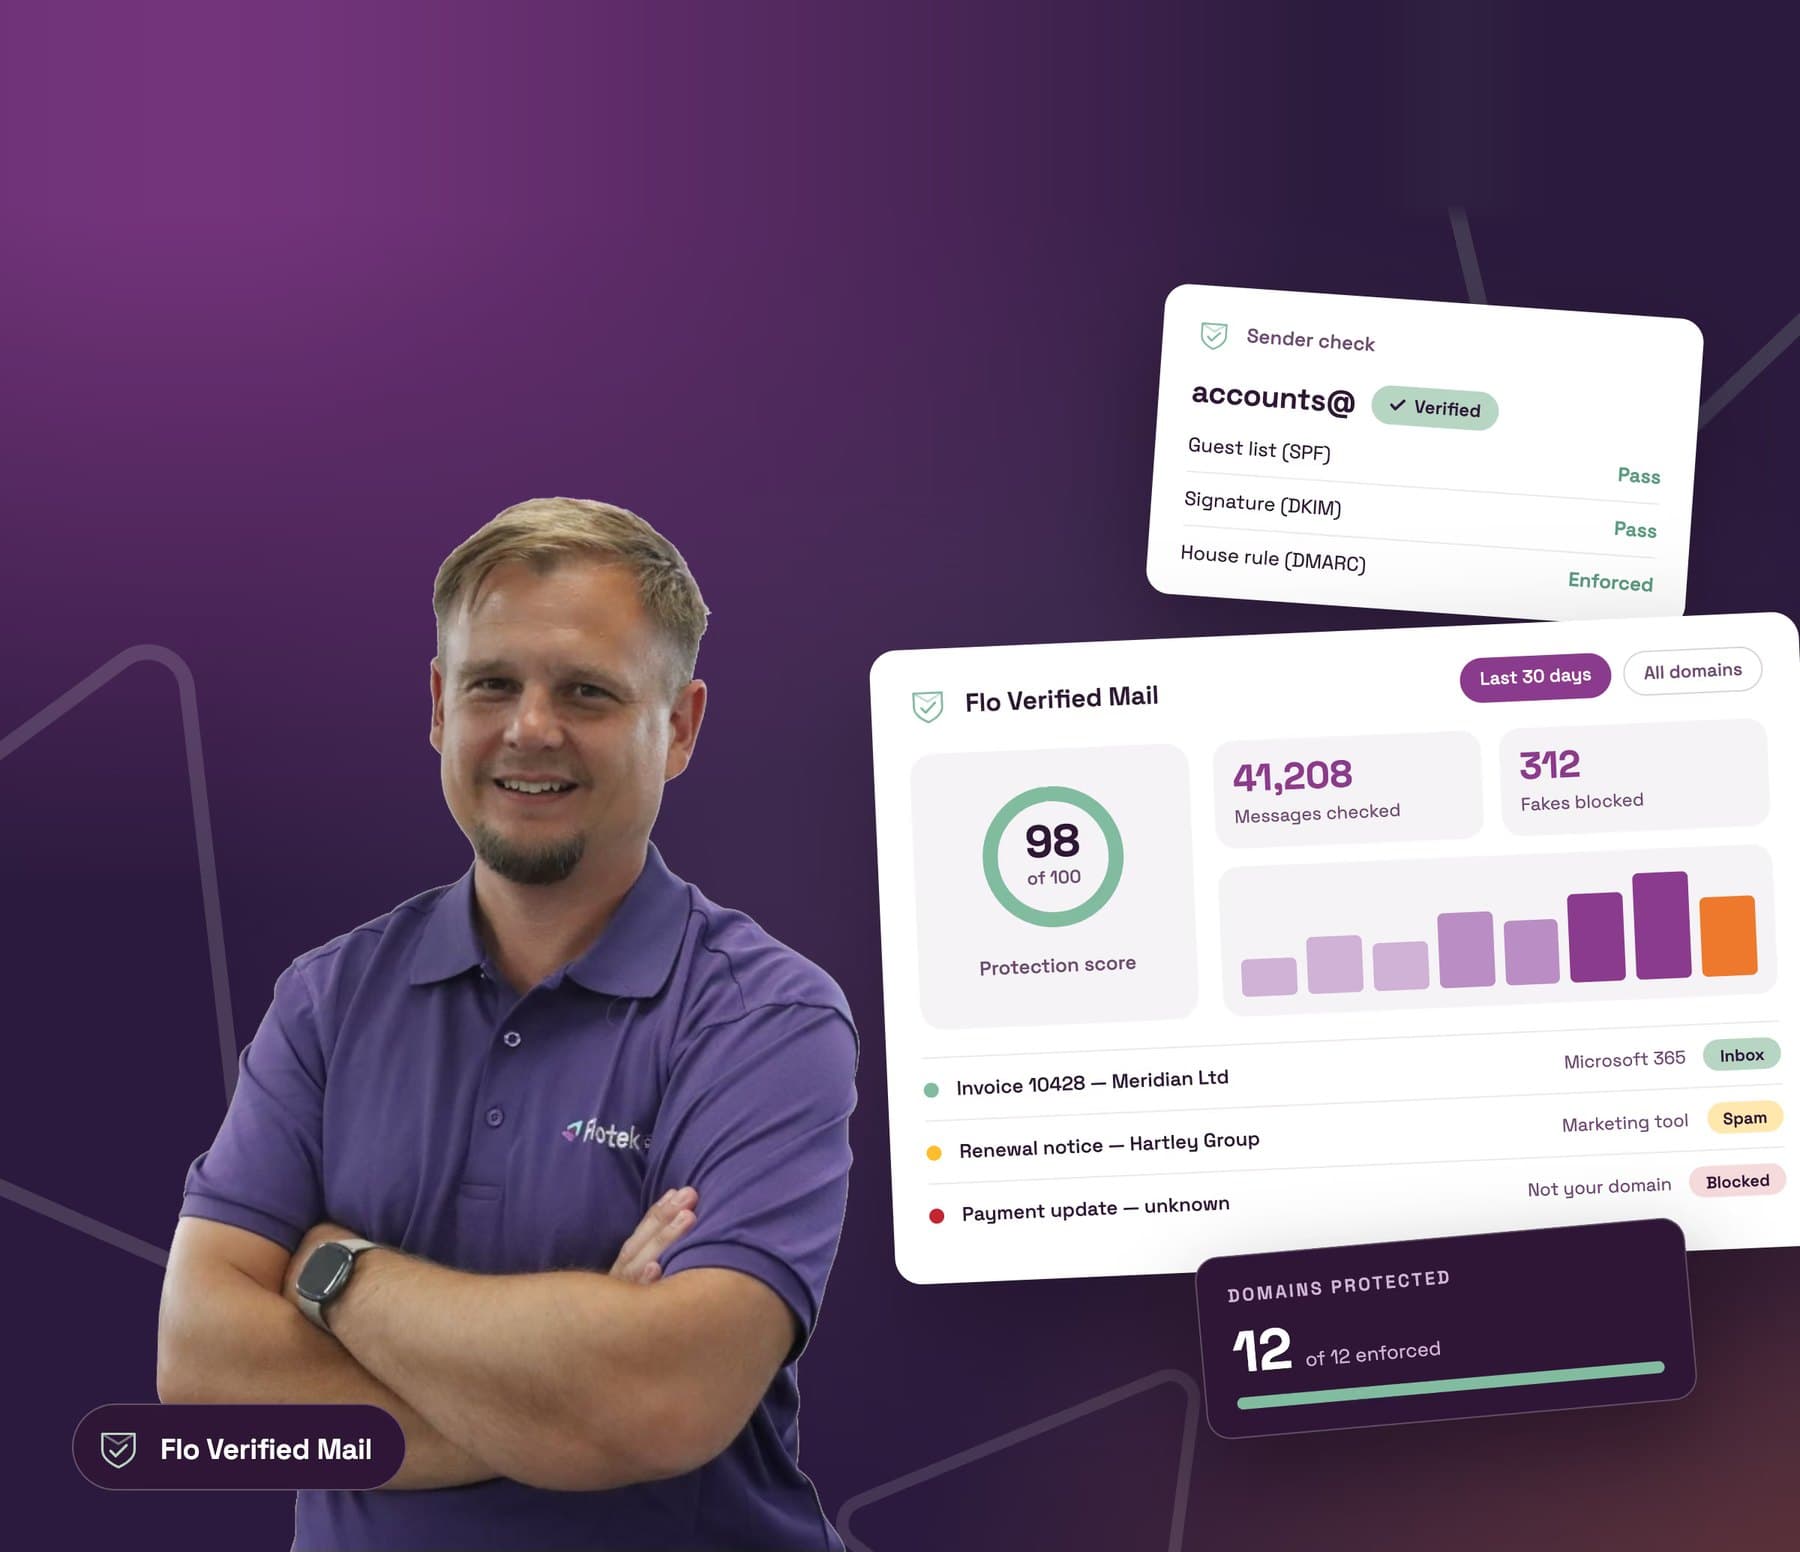
Teams that stopped copying records by hand.Less DNS work. More domains at enforcement.
5.0 out of 5 on G2Trusted by over 10,000 domains
Deliverability
21% more meetings booked.How gaiia stopped landing in spam.
“We increased our meetings booked by 21% and slept better at night knowing our emails are now secured”

Marc-André Campagna, CEO, gaiia


Smart DNS Deployment: FAQ
Does Palisade have write access to my DNS?
Yes. Palisade writes only records you approve, through access you grant yourself. With the one-time sign-in, you approve the records in your DNS provider's own window, and Palisade never sees the password and keeps no access afterwards. With an account connection for Cloudflare, GoDaddy or Amazon Route 53, you create a token or AWS role, and Palisade keeps that access until you disconnect it in Palisade or revoke it at the provider. For Cloudflare and GoDaddy, Palisade stores the token encrypted with AWS KMS and only ever shows its last four characters. For Route 53, it stores no AWS keys at all. A token can allow more than Palisade needs, so Palisade sets the limit in its own code. Palisade writes only email records: SPF, DKIM, DMARC, BIMI, MTA-STS and TLS-RPT, the CNAME or NS records that delegate them, and your mail provider's MX when you ask it to set up mail. It refuses A, AAAA and every other record type.
Which DNS providers does Palisade publish to?
64, covering the registrars and DNS hosts most businesses use, including GoDaddy, Cloudflare, Namecheap, Amazon Route 53, Squarespace and IONOS. The full current list is on this page. Palisade checks which provider answers for your domain and tells you before you start, so you know which path is open to you.
Can Palisade publish a record without my approval?
No. The Agent investigates, drafts the fix, and proposes each step — you approve before anything ships. What this changes is only what happens after you approve: publishing is a click instead of a copy-paste into a provider dashboard.
Do my nameservers or registrar move?
No. Your registrar and nameservers stay exactly where they are, and nothing is transferred. Palisade never takes over your zone; each record you approve is written into the zone you already have.
What if my DNS provider isn't supported?
The record is still generated in full and ready to paste, and monitoring confirms when it goes live. You lose the one-click step, not the fix, and the provider list grows without a release on our side.
How long until a published record is live?
The write itself is immediate, and how quickly resolvers see it depends on the TTL your provider serves. Palisade keeps checking after publishing and confirms when receivers can resolve the record, so a change that did not take becomes a ticket instead of something you find out about weeks later.
How is this different from Hosted DNS?
Smart DNS Deployment is how a record gets published: Palisade writes the approved record into your own zone through the sign-in or account connection you authorise. Hosted DNS is about where the records live afterwards. You point each one at Palisade once, with an SPF include, a CNAME for DMARC, BIMI and MTA-STS, and an NS delegation for DKIM, and Palisade serves them, so later changes take effect without touching your provider at all. Smart DNS Deployment can also publish those delegation records in the first place.
Stop waiting on the DNS ticket
Audit any domain free, no card needed. A card starts the 15-day trial.