Sendmarc
How to migrate from Sendmarc without a reporting gap
 ChatGPT
 Claude
 Gemini
 Perplexity
 Grok
In brief
To migrate from Sendmarc, add a second report recipient, compare both tools for 30 days, then replace the _dmarc CNAME, SPF redirect and DKIM NS records.

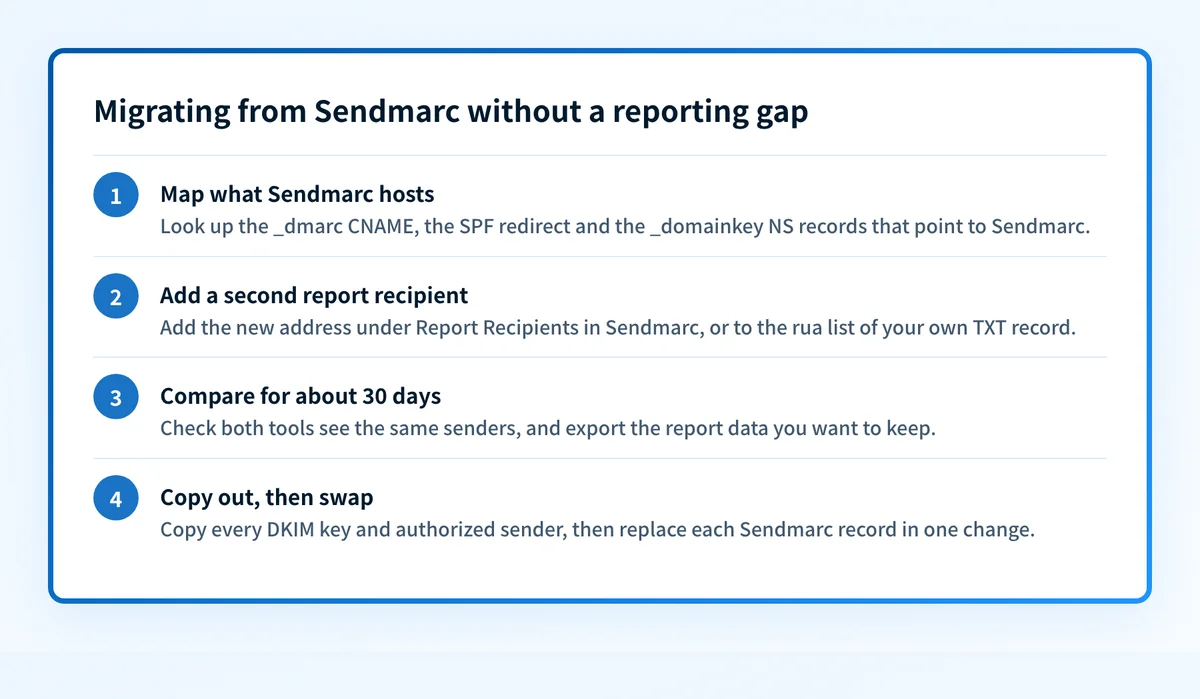
To migrate from Sendmarc without losing reports, run the new tool beside it first. Add the new provider's reporting address as a second report recipient so both tools receive the same aggregate reports, compare them for about 30 days, and only then replace the records Sendmarc hosts for you: usually a _dmarc CNAME to an address under sdmarc.net, an SPF record that redirects to Sendmarc, and NS records that delegate _domainkey to Sendmarc's name servers.
The order matters because Sendmarc answers for those names from its own DNS. If you remove the _domainkey delegation before you have copied the keys behind it, those DKIM selectors stop resolving, and if you replace the SPF redirect before you have rebuilt the sender list, the senders it authorized stop passing SPF.
At a glance
Quick takeaways
- A DMARC record can list more than one aggregate-report address, and Sendmarc's DMARC settings let you add extra report recipients next to its own address, so Sendmarc and another tool can read the same reports at once.
- Sendmarc hosts DMARC by CNAME, SPF through an SPF
redirect=to a Sendmarc-hosted record, and DKIM by NS delegation of_domainkey. MTA-STS, TLS reporting and BIMI can also be CNAMEs into Sendmarc. - Copy every DKIM selector and every authorized sender out of Sendmarc before you change DNS. If SPF flattening is on, rebuild SPF from Sendmarc's sender list, not from the IP addresses its published record may show.
- A name that is delegated by NS, or that holds a CNAME, cannot hold other records beside it, so each swap is one change: remove Sendmarc's record and publish the replacement together.
- Keep the policy tags (
p,sp,np,adkim,aspf, plus anyt,pct,ruf,foorrialready present) exactly as they are during the move. A provider change is not a policy change. - Sendmarc's standard terms renew a subscription for the same term unless you give written notice no later than 30 days before it ends, so check the renewal date on your order form before you start.
Step 1: Find out what Sendmarc hosts for the domain
Sendmarc's help center says it uses "various forms of DNS delegation" for each record (Sendmarc help center, checked 15 November 2026):
| Record | How Sendmarc hosts it | What you see in DNS |
|---|---|---|
| DMARC | CNAME to a raw TXT record on Sendmarc's DNS | _dmarc CNAME to a unique address under sdmarc.net |
| SPF | SPF redirect to a Sendmarc-hosted record | v=spf1 redirect=_youridentifier.sdmarc.net at the apex |
| DKIM | NS delegation of _domainkey | _domainkey NS records for Sendmarc's name servers |
| MTA-STS | CNAMEs for the TXT record and the policy host | _mta-sts CNAME into sdmarc.net, mta-sts CNAME to mta-certs.sendmarc.com |
| TLS reporting | CNAME | _smtp._tls CNAME into sdmarc.net |
| BIMI | CNAME | default._bimi CNAME into sdmarc.net |
Run these lookups for your own domain. Replace example.com with it.
dig +short CNAME _dmarc.example.com
dig +short TXT _dmarc.example.com
dig +short TXT example.com | grep spf1
dig +short NS _domainkey.example.com
dig +short CNAME _mta-sts.example.com
dig +short CNAME mta-sts.example.com
dig +short CNAME _smtp._tls.example.com
dig +short TXT default._bimi.example.com
Any answer that contains sdmarc.net, sendmarc.net or sendmarc.com is a record Sendmarc hosts or reads. So is any _domainkey NS record you did not set up yourself, even one naming Azure DNS name servers (see below). Write each one down with the record it replaces. Sendmarc runs its own domain the same way: on 15 November 2026, _dmarc.sendmarc.com was a CNAME into sdmarc.net, its SPF record was a single redirect= to sdmarc.net, and its mta-sts host was a CNAME to mta-certs.sendmarc.com.
Three patterns cover most domains:
- A
_dmarcCNAME intosdmarc.net. Sendmarc lists this as "Verified": it serves the DMARC record, and you change the policy in Sendmarc, not at your DNS provider (DMARC settings). - A
_dmarcTXT record whoseruaincludes an address atsdmarc.net. Sendmarc calls this "Partial Verification". You manage the record yourself, and Step 2 is a one-line edit. - An SPF record that reads
v=spf1 redirect=followed by ansdmarc.netaddress. The list of senders lives in Sendmarc. Sendmarc also offers an include form for DNS hosts that cannot publish a redirect (SPF settings), so aninclude:intosdmarc.netmeans the same thing.
_domainkey delegation is the one to check by hand. Sendmarc's current guide shows ns1.sendmarc.net and ns2.sendmarc.net (DNS records and delegation), while an older guide shows Azure DNS name servers (delegation records), which is what _domainkey.sendmarc.com itself used on 15 November 2026. If _domainkey has NS records and you did not set them up for another provider, open the domain's DKIM tab in Sendmarc to confirm.
Step 2: Add the second reporting address
The rua tag takes a comma-separated list of addresses (RFC 9989, section 4.7), so both tools can receive the same aggregate reports. In Palisade, the domain's Manage DMARC page generates the record to copy; take the rua address from it (Palisade docs).
When _dmarc is a CNAME to Sendmarc, the record is served from Sendmarc, so you cannot edit it at your DNS provider. Sendmarc's DMARC settings page has a Report Recipients field under Aggregate Report Settings for "additional email addresses to which you would like aggregate feedback to be sent", and Sendmarc keeps its own reporting address in the record by default (Sendmarc help center, checked 15 November 2026). Add Palisade's address there and leave everything else as it is.
When you manage the TXT record yourself, keep every tag and add the second address after the first:
_dmarc.example.com TXT "v=DMARC1; p=quarantine; rua=mailto:a.youridentifier@sdmarc.net,mailto:your-palisade-address@reports.example"Both addresses above are placeholders. Keep the Sendmarc address your record already has, and copy the Palisade address from the record Palisade generates.
Reports sent to an address on another domain need that domain's permission (RFC 9990, section 4). If no reports reach Palisade after two days, check the address was copied exactly, then contact Palisade support.
Step 3: Compare both tools for about 30 days
Aggregate reports usually arrive once a day from each mailbox provider, so a month gives you enough days to see every regular sender, including monthly billing and newsletter runs. During the overlap:
- Confirm both tools list the same sending sources and roughly the same message counts.
- Compare pass and fail rates for each sender. A large gap points to a sender that Sendmarc authorizes in its hosted SPF record and that your new SPF record will need to name.
- Save the report data you want to keep. Sendmarc's Portal API has sender and IP-statistics endpoints on the paid plans (API token guide), or ask Sendmarc support for an export. Its terms let it dispose of your data unless you ask in writing, within ten days after the agreement ends, for a copy of the latest backup (Sendmarc terms of service, section 6.3.3, last updated 5 October 2026), so doing this during the overlap is simpler than asking afterwards.
- Leave the policy alone. If a policy change is due, make it before or after the move, not during it.
Step 4: Copy out what Sendmarc holds, then swap the records
Keep Sendmarc active until each replacement resolves. Work through the records in this order.
- DKIM keys first. Open the domain's DKIM tab in Sendmarc and copy every public key, with its selector and record type. Sendmarc stores each key as either a TXT or a CNAME record (DKIM settings), and both kinds have to move. No DNS query lists every selector, so check your list against the selectors in the aggregate reports you collected during the overlap. If the new home is another provider's delegated zone, add each selector there first; Palisade's hosted DKIM is also a
_domainkeyNS delegation, so a move to Palisade works this way (Palisade hosted DKIM docs). Then switch the_domainkeyNS records in one change. If the new home is your own zone, remove the NS records and add every selector in the same change: while_domainkeyis delegated, selectors under it in your zone do not resolve. A missed selector fails DKIM for that sender. - SPF. Rebuild the record from the Authorized Senders list on the domain's SPF tab in Sendmarc, not from what
digreturns. When SPF flattening is on and the record reaches the lookup limit, Sendmarc can publish the IP addresses behind each include rather than the include itself, and Sendmarc's help center notes that its interface keeps showing each sender's include while the published record carries only the addresses (SPF flattening). Copying those addresses would freeze every sender's IP list on the day you copied it. Check the rebuilt record stays under the 10-lookup limit (RFC 7208, section 4.6.4), then replace the wholeredirect=record with it in one change. In Palisade, hosted SPF is a single include, and you copy every existing mechanism into it before you publish (Palisade hosted SPF docs). - DMARC. Copy the current policy exactly from
dig +short TXT _dmarc.example.com, which follows the CNAME to the record Sendmarc serves. Then, in one change, remove the_dmarcCNAME and publish the new provider's hosted record or your own TXT record. A name that holds a CNAME cannot hold a TXT record beside it, so the two cannot overlap. Keep the same policy tags, including anypct: receivers that still honourpctwill apply the policy to all mail if you drop it. In Palisade, hosted DMARC is a CNAME, and a diff preview shows what changes before you apply it (Palisade hosted DMARC docs). - MTA-STS and TLS reporting. If Sendmarc hosts MTA-STS, repoint the
mta-stshost first and wait untilhttps://mta-sts.example.com/.well-known/mta-sts.txtserves the new policy with a valid certificate and the rightmxlines. Then repoint_mta-sts, which changes theid(RFC 8461, section 8.1). Replace the_smtp._tlsCNAME with the new provider'sv=TLSRPTv1; rua=...TXT record in the same change. With Palisade, TLS reporting is a TXT record in your own zone. - BIMI. If your BIMI record loads its logo or certificate from
portal.sendmarc.com, as Sendmarc's owndefault._bimirecord did when checked withdigon 15 November 2026, host both files at the new provider before you changedefault._bimi. - Verify, then cancel. Run the lookups from Step 1 again. When the only reference to Sendmarc left in DNS is its address in
rua(andruf), and_domainkeyno longer has NS records naming Sendmarc's or Azure DNS name servers, remove that address, delete the domain in Sendmarc, and cancel on your schedule.
A switch from Sendmarc that stops halfway
One unfinished move is easy to miss: two report recipients left in place for months. Both tools keep receiving reports, the Sendmarc subscription renews, and nobody owns the last step because the new tool already looks like it works. If dig +short TXT _dmarc.example.com still shows sdmarc.net next to your new provider long after the overlap, the switch did not finish. Either complete Step 4 or decide on purpose to keep Sendmarc as the second reader.
What changes for an MSP moving many client domains
The method is the same for every client domain, so an MSP can batch it. Group client domains by what Sendmarc hosts: domains with their own TXT record need only the rua edit, while domains with a _dmarc CNAME, an SPF redirect and a _domainkey delegation need the keys and the sender list copied out first. Run the 30-day overlap for a whole group at once, and move the delegations group by group.
Three Sendmarc details matter more at portfolio scale:
- The client subscription. Sendmarc's terms let a channel partner cancel a client's subscription, may apply fees when it ends before its term, and give that client 90 days to move its data to a new Sendmarc subscription, with the partner or with Sendmarc directly. To take data out of Sendmarc, the ten-day backup request in section 6.3.3 is the route (Sendmarc terms of service, appendix 1, clause 4.2).
- The PSA billing lines. Sendmarc's ConnectWise, HaloPSA and Autotask integrations add the Sendmarc package to each client's agreement, recurring invoice or contract services (ConnectWise, HaloPSA, Autotask). Remove or replace that line for each client you move, so the client is not invoiced for a product that is gone.
- The renewal date. Check each order form's term before you start. Unless the order form says otherwise, Sendmarc's terms want written notice of non-renewal no later than 30 days before the term ends (section 6.1).
Related Sendmarc guides
- Sendmarc alternative for MSPs, compared with Palisade
- Sendmarc pricing: what it publishes and what it leaves out
- Sendmarc review: what is confirmed and who it fits
Evidence
Sources and further reading
- Sendmarc help center: DNS records and delegation
- Sendmarc help center: delegation records
- Sendmarc help center: DMARC configuration settings
- Sendmarc help center: SPF configuration settings
- Sendmarc help center: SPF flattening
- Sendmarc help center: DKIM configuration settings
- Sendmarc help center: ConnectWise integration
- Sendmarc help center: HaloPSA integration
- Sendmarc help center: Autotask integration
- Sendmarc help center: create an API token
- Sendmarc terms of service
- RFC 9989: DMARC
- RFC 9990: DMARC aggregate reporting
- RFC 7208: Sender Policy Framework
- RFC 8461: SMTP MTA Strict Transport Security
- Palisade docs: hosted DKIM
- Palisade docs: hosted SPF
- Palisade docs: hosted DMARC
- Palisade docs: updating your DMARC record on your DNS provider
Questions readers ask
Frequently asked questions
Can I run Palisade and Sendmarc at the same time?
Yes. A DMARC record's rua tag can list both tools' reporting addresses, so Palisade and Sendmarc each receive the same aggregate reports. If Sendmarc hosts the record by CNAME, add Palisade's address under Report Recipients in the domain's DMARC settings in Sendmarc. If you manage a TXT record, add the address to the rua list yourself.
How do I know if Sendmarc hosts my DMARC record?
Run dig +short CNAME _dmarc.yourdomain.com. A CNAME ending in sdmarc.net means Sendmarc serves the record and the policy is edited in Sendmarc. A TXT record whose rua includes an sdmarc.net address means you manage the record and Sendmarc only receives reports.
What do I need to copy out of Sendmarc before leaving?
Copy every DKIM public key, with its selector and record type, and the full Authorized Senders list from the domain's SPF tab. Sendmarc serves both while it holds the _domainkey delegation and the SPF redirect, so neither survives the move unless you rebuild it. Save any report data you want to keep as well, through the Portal API or by asking Sendmarc support.
Can I copy my SPF record from DNS when I leave Sendmarc?
Not if SPF flattening is on. Once the record reaches the lookup limit, a flattened Sendmarc record can publish the IP addresses behind each sender instead of the sender's include, so copying it freezes those addresses. Rebuild SPF from the Authorized Senders list in Sendmarc, which keeps each sender's include, and check the result stays under 10 DNS lookups.
Will I lose my DMARC report history when I leave Sendmarc?
Sendmarc's report history does not move to a new tool on its own. Sendmarc's terms let it dispose of your data unless you ask in writing, within ten days after the agreement ends, for a copy of the latest backup, so save what you need during the 30-day overlap, through Sendmarc's Portal API or by asking its support, and ask the new provider whether it can import it.
Does moving off Sendmarc change my DMARC policy?
No. Moving off Sendmarc does not change your DMARC policy as long as you keep p, sp, np, adkim and aspf, plus any t, pct, ruf, fo or ri tags, exactly as they are when you replace the _dmarc CNAME. Changing provider and changing policy are separate changes, and doing both at once makes any delivery problem harder to trace.
Written by
Samuel ChenardCEO & Co-Founder, Palisade
Samuel Chenard is the CEO and co-founder of Palisade, agentic DMARC software for IT teams and MSPs, from one domain to thousands.
More from Samuel →